A blockchain is a shared, append-only database that records transactions in cryptographically linked "blocks" maintained simultaneously across many independent computers, so no single party can quietly rewrite the record. It matters because it lets parties who do not trust each other agree on one version of the truth without a central intermediary. That said, "blockchain" is not one thing: public networks like Bitcoin and Ethereum behave very differently from the permissioned ledgers a single bank runs internally, and the trade-offs between them are the whole story.
The word "blockchain" is now attached to everything from a $2 trillion-plus asset class to supply-chain pilots at Fortune 500 companies, yet most explanations either drown the reader in jargon or collapse the technology into "Bitcoin." This guide separates the two. It covers the precise definition, the step-by-step mechanics of how a transaction becomes an immutable record, the main network types, the cryptography and consensus that keep the system honest, how smart contracts add a programmable layer, the full history from 1991 to the 2024 US spot Bitcoin ETFs, and the concrete benefits, use cases, and limitations institutions weigh today. By the end you will be able to explain, in plain language, what a blockchain actually is and where it is genuinely useful. This is where banks, regulators, and infrastructure providers are now focusing serious attention: MERGE, positioned as Europe's largest crypto and tech event, gathers 3,000+ attendees and 200+ speakers around exactly these questions. Nothing here is investment advice; crypto-asset values fluctuate and can lose value.
In 30 seconds
- What it is. A shared record that only grows, copied at the same time across thousands of computers.
- Why it matters. It lets parties who do not trust each other share a single version of the truth without an intermediary.
- How it stays secure. Hashes that chain the blocks together, digital signatures and a consensus mechanism.
- The nuance. A public network like Bitcoin does not work the same way as a bank's private network.
Blockchain architecture, consensus and scalability are covered in depth in Module 6 of MERGE Institute, Infrastructure and Technology (taught in Spanish). See the programme →
1. Defining Blockchain: What Exactly Is It?
A blockchain is a continuously growing list of records, called blocks, that are linked together and secured using cryptography, and maintained not on one server but across a distributed network of computers. Each block contains a batch of validated transactions, a timestamp, and a cryptographic reference to the block before it. That chain of references is what makes the data tamper-evident: change one block and every block after it visibly breaks.
The financial system does not move money: it synchronises databases that do not talk to each other. Blockchain proposes that every party shares the same ledger.
Why a shared ledger matters: the idea MERGE Institute starts with
The underlying category is distributed ledger technology (DLT): any system where the record of transactions is shared, replicated, and synchronised across multiple locations rather than held by a single authority. Blockchain is the most prominent form of DLT because Bitcoin proved, in 2009, that a purely distributed ledger could resist tampering and double-spending without any trusted central operator.
A useful analogy is a shared document that thousands of people can read at once. Imagine a Google Doc visible to everyone, where every edit is permanently logged, every participant holds an identical copy, and no single person can secretly delete or rewrite a past line without everyone else's copies rejecting the change. A blockchain works like that shared document, except the "editing rules" are enforced by cryptography and a consensus procedure rather than by a company's servers.
This is what separates a blockchain from a conventional database. In a traditional database, a central authority (a company, a bank, a government agency) owns the data, controls who can read and write, and can edit or delete records at will. That is efficient and perfectly appropriate for most business systems, but it requires you to trust the operator. In a blockchain, control is distributed among network participants called nodes. Each node stores a copy of the ledger (the full transaction history), the network follows a shared consensus procedure to agree on what gets added next, and once data is confirmed it carries the property of immutability: it is extraordinarily hard to alter after the fact.
Those four words, nodes, ledger, consensus, and immutability, are the vocabulary the rest of this guide builds on. Keep in mind that none of these properties are absolute; they exist on a spectrum that depends heavily on the specific network's design, which is why the "public versus private" distinction later in this article matters so much.
| Traditional database | Blockchain | |
|---|---|---|
| Who controls the data | A central organisation | The network's nodes, collectively |
| Who can write | Whoever the administrator authorises | Anyone who follows the protocol rules |
| Edit or delete | Yes, at any time | No, new records are only appended |
| Who you trust | The operator | Cryptography and consensus |
| Speed | Very high | Lower, depends on the network design |
| Fits when | A single trusted party runs the system | Several parties who do not trust each other need a shared record |
Traditional database vs. blockchain
1.1 Distributed Ledger Technology (DLT) vs. Blockchain
Distributed ledger technology is the broad umbrella: any technology that distributes identical data records across multiple locations or participants simultaneously, with an agreed mechanism to keep those copies in sync. The defining characteristic is the absence of a single central data store.
Blockchain is one specific type of DLT, the one that organises data into sequential blocks chained by cryptographic hashes. It is not the only design. Directed Acyclic Graphs (DAGs), used by networks such as IOTA and Hedera, structure transactions as an interconnected graph rather than a linear chain, which can allow higher throughput. Hashgraph uses a "gossip about gossip" protocol and virtual voting to reach consensus. R3's Corda, popular in financial services, deliberately omits a global broadcast chain and shares data only with the parties to a given transaction.
The distinction matters for anyone evaluating enterprise solutions. A vendor pitching a "blockchain" may actually be offering a DAG or a permissioned DLT with very different properties for throughput, privacy, and finality. Asking whether data is organised into a globally shared chain of blocks, who runs the nodes, and how consensus is reached tells you far more than the marketing label. In short: all blockchains are distributed ledgers, but not all distributed ledgers are blockchains.
Distributed ledger technology (DLT)
Every blockchain is a DLT, but not every DLT is a blockchain
1.2 The Immutable Ledger: Why "Write Once, Read Many" Matters
Immutability means that once data is confirmed and added to the chain, it cannot be altered or deleted without the agreement of the network. This is often described as a "write once, read many" model: records are appended, never overwritten.
The mechanism behind this is cryptographic hashing. Each block is run through a hash function that produces a fixed-length, unique fingerprint of its contents, and that fingerprint is stored in the next block. If anyone changes even a single character in a historical block, its hash changes, which no longer matches the reference held by the following block, and the mismatch cascades forward through the entire chain. Combined with the fact that thousands of nodes hold identical copies, retroactive editing becomes practically infeasible on a large network.
For institutions, this is the headline feature. An immutable ledger delivers auditability (every record carries a verifiable timestamp and history), fraud reduction (you cannot silently backdate or alter an entry), and support for regulatory compliance (auditors and supervisors can be given read access to a single, tamper-evident source of truth). The caveat, explored in Section 4, is that "immutable" is better understood as "tamper-evident and extremely tamper-resistant" rather than physically impossible to change.
2. How Blockchain Works: A Step-by-Step Breakdown
To see how these properties come together, it helps to follow a single transaction through its full lifecycle, from the moment a user initiates it to the point where it becomes a permanent part of the ledger. The journey involves five distinct players: the user who creates the transaction, the peer-to-peer network that carries it, the nodes that validate it, the consensus procedure that decides which block gets added next, and the chain itself that stores the result. The sections below unpack each stage, starting with the structure of a block, moving through how blocks link into a chain, then walking the end-to-end recording process, and finally explaining the nodes that keep the whole system running without a central server. None of this requires you to trust any single participant, which is precisely the point.
2.1 Anatomy of a Block
A block is the fundamental container of a blockchain, and it has a consistent internal structure. Four components matter most.
Tx C → D · 1.10 BTC
+ 2,481 transactions
- Data. The content: the transactions grouped in the block.
- Hash. The block's unique fingerprint. Change a single character of the data and it changes completely.
- Previous hash. The fingerprint of the previous block. This field is the "chain".
- Nonce. The number miners try again and again under Proof of Work until they find a valid hash.
Anatomy of a block (illustrative values)
Data (the payload). This is the substance of the block: the transaction details. For a cryptocurrency, that means the sender's address, the receiver's address, the amount, and a timestamp. For a supply-chain application, it might be a logged event such as "shipment 4471 cleared customs at 14:32." A single block typically bundles many transactions together.
Hash. Every block has its own cryptographic hash, a unique fixed-length fingerprint generated from the block's contents. Change anything inside the block and the hash changes completely. The hash functions as the block's identity.
Previous block's hash. Each block also stores the hash of the block immediately before it. This single field is the "chain" in blockchain: it is the link that ties each block to its predecessor, forming an unbroken, ordered sequence stretching back to the very first block.
Nonce. In Proof-of-Work systems, the nonce (short for "number used once") is a value that miners repeatedly change in order to produce a block hash that meets the network's difficulty target. Finding the right nonce is the computational "puzzle" that mining solves.
Picture three blocks in a row. Block 1 contains its data, produces Hash A, and (as the first block) has no meaningful previous hash. Block 2 contains its own data, stores Hash A as its "previous hash," and produces Hash B. Block 3 stores Hash B and produces Hash C. The arrows always point backward: data feeds the hash, and each block's hash feeds into the next block's "previous hash" field. That backward-pointing linkage is what makes the structure a chain rather than a mere list.
2.2 How Blocks Are Chained Together
The hash-linking mechanism is the quiet genius of blockchain design. Because each block embeds the hash of the previous block, the blocks are not just stored in order, they are cryptographically dependent on one another.
Consider what happens if a bad actor tries to alter a transaction in, say, Block 3 of a long chain. Changing the data in Block 3 changes Block 3's hash. But Block 4 still stores the old Block 3 hash as its "previous hash" field, so the link is now broken; Block 4 no longer points to a valid predecessor. To repair that, the attacker would have to recompute Block 4's hash, which in turn invalidates Block 5, then Block 6, and so on. The tampering cascades forward through every subsequent block to the tip of the chain.
This cascade is what makes retroactive tampering computationally infeasible on a healthy network. On a Proof-of-Work chain, recomputing all those hashes means redoing the enormous mining work for every affected block, faster than the honest network is extending the legitimate chain. On a Proof-of-Stake chain, rewriting history means controlling a majority of staked value and risking having it destroyed. Either way, the economics are stacked against the attacker. Combine that with the fact that thousands of independent nodes each hold the canonical chain and will simply reject a version that does not match, and you have a ledger that is practically, if not theoretically, impossible to rewrite.
Original chain
Someone tampers with block 2
Block 2's hash changes, block 3 no longer points to it and the break cascades to the end. Hiding it would mean redoing every following block faster than the rest of the network.
Why tampering with one block breaks the whole chain
2.3 The Transaction Recording Process (End-to-End)
Here is the full lifecycle of a transaction, step by step.
- 1InitiationYou sign the transaction with your private key.
- 2BroadcastIt travels from node to node across the P2P network.
- 3ValidationNodes check the signature and the funds.
- 4BundlingIt waits in the mempool and goes into a candidate block.
- 5ConsensusThe network decides which block is added.
- 6AppendedEvery node updates its copy of the ledger.
- 7ConfirmationEach new block on top makes it harder to reverse.
On Bitcoin, about six confirmations (around an hour) are enough to treat a payment as settled with very high confidence.
A transaction's journey in 7 steps
Step 1: Initiation. A user creates a transaction, for example sending cryptocurrency from their wallet to someone else's, or logging a supply-chain event. They sign it with their private key, which cryptographically proves they authorised it (more on this in Section 4).
Step 2: Broadcast. The signed transaction is broadcast to the peer-to-peer (P2P) network. There is no central server to send it to; instead the transaction propagates from node to node across the network.
Step 3: Validation. Nodes independently check the transaction against the network's agreed rules: Is the signature valid? Does the sender actually have the funds? Does the transaction follow the protocol's format? Invalid transactions are discarded.
Step 4: Bundling. Validated transactions wait in a pool (often called the mempool). A node preparing to add to the chain gathers a batch of these transactions into a candidate block.
Step 5: Consensus. The network runs its consensus mechanism (covered in detail in Section 5) to agree on which candidate block becomes the next official block. Under Proof of Work, miners compete to solve the puzzle; under Proof of Stake, a validator is selected to propose the block and others attest to it.
Step 6: Appending and propagation. The winning block is appended to the chain and broadcast across the network. Every node updates its local copy of the ledger to include the new block.
Step 7: Immutable recording. The transaction is now part of the chain. As more blocks are added on top of it, it becomes progressively harder to reverse, which is why merchants and exchanges wait for a number of "confirmations" before treating a payment as final. There is a second reason: occasionally two miners find a block almost at once and the chain forks briefly. Waiting a few blocks (six is the convention on Bitcoin, roughly an hour) lets those short branches die out so the whole network converges on the chain with the most accumulated work.
A concrete example: suppose wallet A sends Bitcoin to wallet B. Wallet A signs the transaction and broadcasts it. Nodes confirm that wallet A controls enough unspent bitcoin and that the signature is genuine. A miner includes the transaction in a candidate block, solves the Proof-of-Work puzzle, and broadcasts the solved block. Every node adds it. After roughly an hour (six blocks, at about ten minutes each), the payment is considered settled with very high confidence. At no point did a bank, a payment processor, or any central party approve the transfer; the network did it collectively.
2.4 Nodes: The Backbone of the Network
A node is any computer that participates in the blockchain network by running its software and communicating with other participants. Nodes are the backbone of decentralisation: they are the reason there is no central server to shut down or compromise.
There are several types. Full nodes download and store the entire blockchain, independently verify every transaction and block against the consensus rules, and reject anything invalid. They are the enforcers of the protocol. Light nodes (also called SPV, or Simplified Payment Verification, nodes) store only block headers rather than the full chain, relying on full nodes for detailed data; this lets them run on phones and low-powered devices. Mining or validator nodes are the specialised nodes that actively produce new blocks, either by mining under Proof of Work or by staking and attesting under Proof of Stake.
Collectively, these nodes maintain the ledger without any central coordinator. Each full node holds its own complete copy and enforces the rules independently, so the "truth" of the network is simply the version that the majority of honest nodes agree on and will accept. The more geographically and politically dispersed the nodes, the harder the network is to censor, capture, or switch off.
The largest conference on crypto and digital assets
Banks, fintechs and the crypto ecosystem at the same table. Two editions in 2027:
3. Key Features and Properties of Blockchain
3.1 Blockchain Decentralization
Decentralisation means that no single entity owns, operates, or controls the ledger. Authority over what the network records and how it evolves is distributed among many independent participants rather than concentrated in one institution.
In practice, decentralisation is a spectrum rather than a binary. At one end sit fully decentralised networks such as Bitcoin, where tens of thousands of nodes worldwide run the software, no company can unilaterally change the rules, and no one needs permission to participate. In the middle are consortium or federated chains, where a defined group of organisations jointly governs the network, a model common in banking and trade finance. At the other end are private chains operated by a single organisation that merely distributes storage across several of its own servers; these gain some resilience benefits but retain centralised control.
Why does decentralisation matter? First, it eliminates single points of failure: there is no central database to hack, corrupt, or take offline, because the ledger lives on many machines at once. Second, it provides censorship resistance: no single party can block a valid transaction or freeze an account on a sufficiently decentralised network. Third, it enables trustless interaction, meaning two parties who have never met and have no reason to trust each other can nonetheless transact with confidence, because the protocol and the collective network, not a vulnerable intermediary, guarantee the outcome. The trade-off is that greater decentralisation generally costs speed and efficiency, which is precisely the tension that drives the design of private and consortium chains.
Decentralisation is a spectrum, not a yes or no
3.2 Blockchain Transparency
On public blockchains, transparency is radical: every transaction is visible to anyone with an internet connection. Tools called block explorers, such as Etherscan for Ethereum or the various Bitcoin explorers, let anyone inspect the full transaction history of any address, trace the flow of funds, and verify balances in real time. Nothing is hidden behind a corporate login.
That transparency coexists with pseudonymity, a distinction that is frequently misunderstood. Blockchain addresses are not automatically linked to real-world identities. An address is a string of characters, not a name. So while the complete transaction history of an address is public, who controls that address is not revealed by the blockchain itself. This is pseudonymity (identifiable but not named), not true anonymity. In practice, sophisticated chain-analysis firms and regulated exchanges performing identity checks can often connect addresses to individuals, so users should not assume blockchain activity is private.
Handled well, this combination enables accountability without wholesale surrender of privacy. A regulator or auditor can verify that funds moved as claimed without a trusted intermediary vouching for it, while architectures that add privacy features (such as zero-knowledge proofs) can prove a statement is true without exposing the underlying data. The right design lets a network be transparent about what happened while remaining selective about revealing who did it and the sensitive details involved.
3.3 Openness and Permissionless Access
Closely related to decentralisation is permissionlessness. On a permissionless network, anyone can join as a node, send transactions, or build applications without asking any gatekeeper for approval. There is no account to be granted, no onboarding committee, no central party that can revoke your right to participate. Bitcoin and Ethereum are permissionless.
This contrasts with permissioned (private or consortium) networks, where access is gated: participants are known, vetted, and admitted by an operator or a governing group. Permissioned designs suit regulated environments where participants must be identifiable, but they sacrifice the open-access property.
The innovation implications of openness are significant. Permissionless networks are typically composable, meaning applications can plug into one another like building blocks; a new protocol can build directly on top of an existing one without a partnership agreement. They are usually open-source, so anyone can read, fork, and improve the code. And they gave rise to decentralised finance (DeFi), where lending, trading, and other financial services run as open protocols that anyone can access or build upon. This openness accelerates experimentation, though it also raises genuine questions about consumer protection and regulatory oversight, which is why frameworks such as the EU's Markets in Crypto-Assets Regulation have become central to the institutional conversation.
3.4 Cryptography: The Technical Foundation
Cryptography is what makes everything above possible. Three cryptographic building blocks do the heavy lifting.
Hash functions. A cryptographic hash function takes any input and produces a fixed-length output (the hash) that is unique to that input, practically impossible to reverse, and changes completely if the input changes even slightly. Bitcoin uses SHA-256; Ethereum uses Keccak-256. Hashes are what give each block its fingerprint and what link blocks into a tamper-evident chain, as described earlier.
Public-key (asymmetric) cryptography. Every user has a key pair: a public key, which can be shared freely and from which their address is derived, and a private key, which must be kept secret. When a user wants to send funds, they sign the transaction with their private key. Anyone can then verify, using the corresponding public key, that the signature is genuine, without the signer ever revealing the private key itself. This digital signature proves ownership and authorises the transaction. Lose the private key and you lose access to the funds; there is no central administrator to reset it.
Merkle trees. Rather than hashing a block's many transactions in one unwieldy lump, blockchains organise them into a Merkle tree: transactions are hashed in pairs, then those hashes are hashed together, and so on, until a single hash remains at the top, the Merkle root. This root is stored in the block header and acts as a compact summary of every transaction in the block. Merkle trees make verification efficient: a light node can confirm that a specific transaction is included in a block by checking a short "Merkle proof" rather than downloading every transaction. This elegant structure is one of the reasons blockchains can scale verification to millions of transactions.
Two hashes are enough to prove Tx C is in the block, without downloading the other transactions
4. Blockchain Security: How the Network Stays Trustworthy
4.1 Public Key Cryptography and Digital Signatures
Security on a blockchain begins with asymmetric encryption, the public/private key system introduced above. The public key acts like an account number you can share with anyone so they can send you funds; the private key is the secret that lets you spend them. Crucially, the public key can be derived from the private key, but not the other way around, which is why sharing your public key (or address) is safe while sharing your private key is catastrophic.
A digital signature is how the system proves authorisation without exposing the secret. When you initiate a transaction, your wallet uses your private key to generate a signature that is mathematically bound both to your key and to the exact contents of that transaction. Any node can verify, using your public key, that the signature could only have been produced by the holder of the matching private key, and that the transaction has not been altered since it was signed. In effect, the signature says "I, the holder of this private key, authorised exactly this transaction," and it does so without ever revealing the key.
The public key is derived from the private key, but not the other way round. That is why sharing your address is safe and sharing your private key means losing your funds: "not your keys, not your coins".
How a digital signature proves you authorised a transaction
Wallet addresses are, in most designs, derived from hashed public keys. This adds a layer of protection: your raw public key is not exposed until you actually spend from an address, and the address itself is a shorter, more manageable string. The practical upshot for users is stark: control of the private key is control of the funds. This is the origin of the phrase "not your keys, not your coins," and it is why key management, custody, and secure storage are among the most serious topics in institutional digital assets.
4.2 The 51% Attack: The Primary Threat Vector
The best-known attack against a blockchain is the 51% attack. It occurs when a single actor gains control of the majority of a network's hash rate (under Proof of Work) or staked value (under Proof of Stake), which lets them temporarily outpace the honest network, reorganise recent blocks, and rewrite short stretches of history, typically to double-spend coins they have already sent.
On a large, established network, this is economically prohibitive. Controlling 51% of Bitcoin's global hash rate would require acquiring and powering a staggering quantity of specialised mining hardware, at a cost running into billions of dollars, plus enormous ongoing electricity bills, all to execute an attack that would likely crash the value of the very asset being stolen. The incentives are designed so that honest mining is more profitable than attacking.
Smaller chains are a different story, and they serve as cautionary examples. Ethereum Classic, a smaller Proof-of-Work network, was hit repeatedly in 2020. At 10:57 PM PST on 31 July 2020, Ethereum Classic was 51% attacked resulting in roughly 800,000 ETC (around $5.8 million) of double-spend transactions, and at 8:15 PM PST on 5 August 2020 it was attacked again, resulting in roughly 460,000 ETC (around $3.2 million) of double-spend transactions. Analysts found the economics shockingly cheap: forensic firm Bitquery estimated the attacker made off with 807,260 ETC, having spent roughly 17.5 bitcoins worth about $192,000 on renting hash power to execute the attack. The lesson is that a blockchain's security is proportional to the cost of attacking it, which in turn scales with the network's size and value. Small networks that rent hash power cheaply are far more vulnerable than giants like Bitcoin.
51% attack on Ethereum Classic, 2020
A blockchain is only as secure as it is expensive to attack. On a small network, that cost can be very low.
4.3 Sybil Resistance and Consensus as a Security Layer
A Sybil attack is an attempt to subvert a network by flooding it with a large number of fake identities or nodes, so that one actor controls a disproportionate share of the network while appearing to be many independent participants. In a naive voting system, whoever can spin up the most identities wins.
Blockchains defend against this by making participation costly, and this is one of the central jobs of a consensus mechanism. Under Proof of Work, influence over the next block is tied not to how many identities you run but to how much computational work (and therefore electricity and hardware) you contribute; creating a thousand fake nodes gets you nothing without a thousand nodes' worth of real computing power. Under Proof of Stake, influence is tied to how much capital you have locked up as a stake; fake identities with no stake carry no weight. In both cases, the mechanism converts "one identity, one vote," which is cheap to fake, into "one unit of scarce resource, one vote," which is expensive to fake.
This is why network size and value translate directly into security. The more honest hash power or staked capital securing a chain, the more a would-be attacker must acquire to gain majority control, and the more they stand to lose if they fail or if the attack destroys the asset's value. Consensus is not just a way to agree on the ledger; it is the economic moat that keeps the whole system Sybil-resistant and trustworthy.
4.4 Tamper-Resistance vs. Absolute Immutability
It is more accurate to describe a blockchain as tamper-evident and tamper-resistant than as perfectly immutable. The distinction is not pedantic; it goes to the heart of how these systems are actually governed.
The clearest case study is The DAO. In 2016, The DAO was a high-profile investment fund built as a smart contract on Ethereum, and it held a very large share of all ether in existence at the time. On 17 June 2016, a reentrancy bug in The DAO's smart contract was exploited, stealing 3.6 million ETH, about one-third of its funds, which led to a hard fork in Ethereum, creating two blockchains: Ethereum and Ethereum Classic. The amount at stake was enormous: the hack drained as much as $60 million worth of ether, and even after a white-hat counterattack the stolen funds ultimately amounted to around 5% of all the Ethereum tokens in existence at the time.
Faced with this, the Ethereum community did something striking: it changed the ledger. On 20 July 2016, at a block height of 1.92 million, Ethereum introduced an irregular state change via a hard fork in an effort to return approximately 3.6 million ether that had been taken from The DAO. In other words, the "immutable" ledger was deliberately rewritten by social consensus. Those who rejected this intervention on principle kept running the original chain, which became Ethereum Classic.
This episode illustrates two layers of a blockchain. Below sits technical immutability: the cryptographic cost of rewriting history. Above it sits a governance and social-consensus layer: the humans who run the nodes and can collectively agree to change the rules. The phrase "code is law" captures the ideal that a smart contract's outcome should stand no matter what, even if exploited; the DAO fork showed that in practice a determined community can override code when the stakes are high enough. Which approach is "correct" remains one of the most debated questions in the field, and it is a reminder that immutability is ultimately a property the network chooses to uphold, not a law of physics.
5. Consensus Mechanisms: How Blockchain Networks Agree
5.1 What Is a Consensus Mechanism?
A consensus mechanism is the set of rules and procedures by which the distributed nodes of a network agree on the valid, current state of the ledger, specifically, which transactions are legitimate and which block gets added next. It is the coordination engine that turns thousands of independent computers into a single, coherent record.
Consensus is necessary because a blockchain operates in a trustless environment. There is no central referee to settle disputes, so when two nodes see conflicting information (for example, two competing candidate blocks), the network needs an objective, verifiable, and tamper-resistant way to decide which one is valid. A good consensus mechanism makes honest participation the most rational choice and makes dishonest behaviour expensive or self-defeating. The various mechanisms below are different answers to the same fundamental question: how do strangers agree on the truth without a boss?
5.2 Proof of Work (PoW)
Proof of Work is the original consensus mechanism, introduced by Bitcoin. In PoW, specialised nodes called miners compete to solve a computationally expensive mathematical puzzle: they repeatedly adjust the block's nonce and hash the block until they find a hash that meets the network's difficulty target. The first miner to find a valid solution broadcasts the block, earns the right to add it to the chain, and receives a reward (newly minted coins plus transaction fees).
The security guarantee flows directly from this expenditure. Because adding a block requires real, costly computation, rewriting history would mean redoing that work for every block since the point of attack, faster than the entire honest network can extend the legitimate chain. The deeper a block is buried, the more astronomically expensive it becomes to reverse. This is what makes an established PoW chain so robust.
The drawbacks are equally well known. PoW is energy-intensive by design, since security is literally purchased with electricity; Bitcoin's network consumes power on the scale of a mid-sized country. It also tends toward centralisation of mining into large pools and industrial operations that can afford the cheapest electricity and the most efficient hardware. And it is relatively slow: Bitcoin processes a limited number of transactions per block, with a new block roughly every ten minutes. Bitcoin remains the canonical PoW example and, for its proponents, the security and simplicity of Proof of Work are features worth their cost.
5.3 Proof of Stake (PoS)
Proof of Stake replaces computational competition with economic collateral. Instead of miners burning electricity, validators lock up ("stake") a quantity of the network's cryptocurrency as a bond. The protocol then selects validators probabilistically, weighted by the size of their stake, to propose and attest to new blocks. Honest validation earns rewards; the stake is what gives validators skin in the game.
The headline advantage is energy efficiency. Ethereum's transition to Proof of Stake, known as The Merge, is the landmark example. The Merge completed Ethereum's transition to proof-of-stake consensus in September 2022, officially deprecating proof-of-work and cutting the network's energy use by about 99.95%. The Merge was Ethereum's transition from Proof of Work to Proof of Stake on 15 September 2022, eliminating energy-intensive mining while aiming to improve security and scalability.
The mechanism that keeps PoS validators honest is slashing: if a validator behaves maliciously (for example, by trying to validate two conflicting versions of history) or is seriously negligent, the protocol destroys part or all of their staked collateral. This turns dishonesty into a direct financial loss, replacing the "waste electricity to attack" deterrent of PoW with a "lose your capital to attack" deterrent. Ethereum's shift from PoW to PoS at The Merge was years in the making and is the most consequential consensus change in the industry's history, demonstrating that a major network could swap its security engine while running live. Critics counter that PoS can favour large holders and raises its own questions about validator concentration, which is why the design of staking, slashing, and validator distribution remains an active area of research.
5.4 Other Notable Consensus Mechanisms
Beyond PoW and PoS, several other mechanisms address specific needs.
Delegated Proof of Stake (DPoS). Token holders vote to elect a small set of delegates who produce blocks on the network's behalf. This can deliver high throughput at the cost of greater centralisation, since relatively few delegates hold block-production power. EOS and TRON use variants of DPoS.
Proof of Authority (PoA). A limited number of pre-approved, identified validators secure the network based on their reputation and authority rather than stake or work. This is fast and efficient but relies on trusting those validators, which makes it well suited to private and consortium chains. VeChain and some Hyperledger configurations use PoA-style approaches.
Practical Byzantine Fault Tolerance (PBFT). A classical consensus approach in which known nodes exchange messages in rounds to agree on each block, tolerating a limited fraction of faulty or malicious nodes. It offers low latency and immediate finality, making it a fit for permissioned enterprise networks such as Hyperledger Besu, which uses BFT variants like QBFT.
Proof of History (PoH). Solana's novel contribution, a cryptographic clock that creates a verifiable ordering of events over time, allowing the network to agree on sequence efficiently and support very high throughput, used alongside a Proof-of-Stake system.
A rough comparison helps place them. On energy use, PoW is high while PoS, PoA, PBFT, and PoH are all low. On speed, PoW is slow, PoS is moderate, and DPoS, PoA, PBFT, and PoH are fast. On decentralisation, PoW and PoS tend to be the most open, while DPoS, PoA, and PBFT trade decentralisation for performance. On security model, PoW relies on computational cost, PoS on economic stake, and PoA on trusted identity. There is no single "best" mechanism; each represents a different point on the trade-off surface between decentralisation, security, speed, and energy.
| Mechanism | Security based on | Energy | Speed | Decentralisation | Examples |
|---|---|---|---|---|---|
| Proof of Work | Computational cost | High | Slow | High | Bitcoin |
| Proof of Stake | Locked capital (stake) | Low | Medium | High | Ethereum |
| Delegated PoS | Elected delegates | Low | Fast | Lower | EOS, TRON |
| Proof of Authority | Validator identity | Low | Fast | Low | VeChain |
| BFT (PBFT, QBFT) | Voting among known nodes | Low | Fast | Low | Hyperledger Besu, Cosmos |
| Proof of History | Cryptographic clock alongside PoS | Low | Very fast | Tied to PoS | Solana |
The main consensus mechanisms, compared
6. Types of Blockchain Networks
6.1 Public Blockchain
A public blockchain is open to anyone, fully decentralised, and permissionless. Anyone can download the software, run a node, read the ledger, submit transactions, and, depending on the design, participate in consensus, all without approval from any central party.
The best-known examples are Bitcoin, Ethereum, Litecoin, and Solana. These networks are maintained by thousands of distributed participants and secured by robust consensus mechanisms.
Public blockchains are best suited to use cases where openness and censorship resistance are the whole point: cryptocurrency, open DeFi protocols, NFTs, and applications that must remain accessible regardless of any single authority's wishes. The trade-offs are real. Public chains are generally slower and less private than centralised alternatives, since every transaction is processed and stored across the network and visible to all, and their permissionless, pseudonymous nature can make certain regulatory requirements harder to satisfy, which is one reason regulated institutions often combine public-chain settlement with compliance tooling layered on top.
6.2 Private Blockchain
A private blockchain is controlled by a single organisation. It is permissioned, meaning participants must be invited, known, and vetted, and the operator decides who can read, write, and validate. It is, in essence, a distributed database with blockchain-style cryptographic integrity but centralised governance.
Typical implementations are built on frameworks such as Hyperledger Besu (Ethereum-compatible and now the most widely used), Hyperledger Fabric or R3's Corda, deployed within a company's own environment.
Private chains are best for enterprise record-keeping, internal auditing, and processes such as supply-chain tracking within a single organisation, where the participants are all part of or trusted by one entity. The trade-off is explicit: a private chain sacrifices decentralisation (and therefore censorship resistance and trustlessness) in exchange for speed, privacy, and control. Because one operator runs the show, you must trust that operator, which somewhat undercuts the "trustless" promise, but for many internal enterprise use cases that is an entirely acceptable and even desirable trade.
6.3 Consortium (Federated) Blockchain
A consortium or federated blockchain is governed not by a single company or by the open public but by a pre-selected group of organisations that jointly run the network. Validation rights and governance are shared among these members, striking a middle ground between the openness of public chains and the single-operator control of private ones.
Examples include Quorum (originally developed at JPMorgan), R3 Corda deployments used by banking consortia, and the Energy Web Chain in the energy sector. Today most new consortium projects choose Ethereum-compatible (EVM) technology, and more and more anchor themselves to a public network to inherit its security.
Consortium chains are best for industry-wide data sharing where multiple organisations need a common, trusted ledger but none is willing to let a competitor or a single vendor control it. Classic use cases include trade finance, shared healthcare records, and interbank settlement, where a group of banks or firms operate the network collectively. This model is especially relevant to regulated finance, because it combines the efficiency and privacy institutions require with distributed governance that no single member can abuse.
6.4 Hybrid Blockchain
A hybrid blockchain combines elements of public and private chains, allowing an organisation to keep certain data and processes private while exposing others publicly. The design lets a business control access to sensitive information while still benefiting from the transparency and verifiability of a public ledger for the parts that should be open.
The Dragonchain architecture is often cited as a hybrid design, and IBM Food Trust, built on Hyperledger, uses selective transparency so that participants share only the data each counterparty is entitled to see while still proving the integrity of the overall record.
Organisations typically choose hybrid architecture when they need the public verifiability and trust of an open chain for some interactions (such as proving provenance to a consumer) but must keep commercially sensitive details (such as pricing or supplier terms) confidential. It is a pragmatic answer for enterprises that want the credibility of public anchoring without fully exposing their operations.
| Public | Private | Consortium | Hybrid | |
|---|---|---|---|---|
| Who participates | Anyone, no permission needed | Only invitees of one organisation | A selected group of institutions | Depends on the data: partly open, partly closed |
| Who governs | The network as a whole | One organisation | The members, jointly | The organisation that designs it |
| Privacy | Everything visible (pseudonymous) | High | High among members | Selective |
| Speed | Lower | High | High | Variable |
| Examples | Bitcoin, Ethereum, Solana | Hyperledger Besu, Hyperledger Fabric | Quorum, Energy Web Chain | Dragonchain, IBM Food Trust |
| Best for | Crypto, DeFi, NFTs | Internal records and auditing | Trade finance, interbank settlement | Traceability with private commercial data |
The four types of blockchain network at a glance
6.5 Sidechains and Layer-2 Solutions
As base-layer blockchains hit capacity limits, two families of scaling approaches have emerged.
Sidechains are separate, independent blockchains connected to a main chain by a two-way "peg" that lets assets move between them. They run their own consensus and can have different performance characteristics, offloading activity from the main chain. The Liquid Network, pegged to Bitcoin, is a well-known example.
Layer-2 solutions, by contrast, are built directly on top of a base layer (Layer 1) and inherit its security while processing transactions off the main chain. The main categories are rollups (which bundle many transactions off-chain and post compressed proofs or data back to Layer 1, including optimistic rollups and zero-knowledge rollups), state channels (which let parties transact privately off-chain and settle only the final result on-chain), and plasma (an earlier framework for off-chain child chains).
These approaches matter because they extend the capabilities of base-layer blockchains, dramatically increasing throughput and lowering fees while anchoring security to the underlying Layer 1. Layer-2 scaling, zero-knowledge proofs, and interoperability between chains are among the most active frontiers in the field, and they are exactly the kind of infrastructure topic covered under the Blockchain Infrastructure and Emerging Technologies track at MERGE Madrid, one of its six tracks across three stages, where protocol teams and institutional builders compare what is actually live in production.
MERGE Institute
Learn crypto and digital assets from the leaders of the ecosystem
A 12-week programme, taught in Spanish by working professionals. Blockchain architecture, consensus and scalability are covered in Module 6.
Try a free class →
7. Smart Contracts Explained: Blockchain's Programmable Layer
7.1 What Is a Smart Contract?
A smart contract is self-executing code stored on a blockchain that automatically enforces the terms of an agreement when predefined conditions are met. Rather than relying on a bank, a lawyer, or an escrow agent to carry out an agreement, the logic is written into code that runs exactly as programmed, visible to all and beyond the unilateral control of any single party.
The intellectual origin predates blockchain. Computer scientist and legal scholar Nick Szabo proposed the concept of smart contracts in 1994, long before a platform existed that could run them, envisioning agreements embedded in code that would execute automatically.
The classic analogy is a vending machine. You insert the correct coins and press a button, and the machine automatically dispenses your item, no cashier, no intermediary, no discretion. The "contract" (pay this amount, receive this item) is enforced by the machine's mechanism. A smart contract generalises this idea to arbitrary logic on a blockchain: specify the conditions and the outcomes, deploy the code, and the network executes it faithfully whenever the conditions are triggered. The important nuance is that a smart contract does only what its code says, no more and no less, which is both its great strength and, as we will see, its central risk.
A smart contract is an "if this happens, do that" rule that enforces itself
7.2 How Smart Contracts Work on the Blockchain
Smart contracts have a clear lifecycle. Deployment comes first: a developer writes the contract in a language such as Solidity (for Ethereum), compiles it, and sends it to the blockchain as a special transaction. Once included in a block, the contract lives at its own unique address on the chain, like an autonomous account made of code.
Execution follows: any user, or any other smart contract, can trigger the contract's functions by sending a transaction to its address, optionally with data and funds. The network then runs the contract's code according to its logic.
The guarantee that makes this trustless is determinism. Every node on the network executes the same contract code with the same inputs and must arrive at exactly the same result; otherwise the network could not agree on the new state. This determinism is what allows strangers to rely on a smart contract's outcome without trusting each other or any operator: the result is reproducible and verifiable by the entire network.
On Ethereum, computation is priced through gas fees. Every operation a contract performs costs a certain amount of gas, which the user pays for in ether. Gas serves two purposes: it compensates validators for the computational resources they expend, and it prevents abuse, because an infinite loop or a wasteful contract would cost a prohibitive amount of gas and simply run out before it could harm the network. This economic metering is essential to keeping a shared, Turing-complete computer stable and spam-resistant. Together, deployment, deterministic execution, and gas-based pricing turn a blockchain from a passive ledger into a programmable platform, the foundation of DeFi, tokenization, and much of the emerging digital-asset economy.
7.3 Smart Contract Use Cases
Smart contracts power a growing range of applications.
Decentralised finance (DeFi). This is the most mature category. Smart contracts run automated lending and borrowing markets, decentralised exchanges, and liquidity provision without a bank or broker in the middle. Protocols such as Uniswap (automated trading) and Aave (lending and borrowing) are entirely governed by code that holds and routes billions in assets.
NFTs (non-fungible tokens). Smart contracts define the ownership, provenance, transfer rules, and even ongoing royalties of unique digital items, enabling verifiable digital ownership and programmable resale terms.
Supply-chain automation. Contracts can release payment automatically once an oracle or IoT sensor confirms that goods have been delivered or that a shipment reached a checkpoint, reducing disputes and manual reconciliation.
Insurance. Parametric policies pay out automatically when a trusted data source (an oracle) reports that a defined trigger has occurred, for example a flight delayed beyond a threshold or rainfall below a certain level, removing the claims-processing delay.
Voting and governance. On-chain voting systems use smart contracts to tally votes transparently and tamper-resistantly, which underpins the governance of DAOs and many protocols.
One especially consequential category for institutions is tokenization, representing real-world assets such as funds, bonds, or securities as tokens governed by smart contracts. This is where smart contracts meet regulated capital markets, and it is the focus of a dedicated Tokenization and Capital Markets track at MERGE Madrid, where asset managers and market-infrastructure providers compare what is live under Europe's evolving regulatory frameworks.
7.4 Limitations and Risks of Smart Contracts
Smart contracts carry real risks that any serious user must understand.
The "code is law" principle is a double-edged sword. Because the code executes exactly as written and is difficult to alter, a bug is not just a defect, it is an exploitable vulnerability that an attacker can trigger and that may be impossible to patch in time. The DAO is the defining example: a vulnerability in The DAO, a decentralized autonomous organization on the Ethereum blockchain, allowed a hacker to siphon off tens of millions of dollars in ether, an incident that drained roughly $60 million and ultimately split the Ethereum network.
The oracle problem is another fundamental limit. Smart contracts cannot natively access data from outside their blockchain; they only know what is on-chain. To react to real-world events (a price, a weather reading, a delivery confirmation), they depend on oracles, third-party services that feed external data in. This reintroduces an element of trust and a potential point of failure or manipulation, which is why robust, decentralised oracle design is a major research area.
Upgradability is also challenging. The same immutability that makes contracts trustworthy makes them hard to fix. Developers use complex patterns such as proxy contracts to allow upgrades, but these add their own risks and can reintroduce centralised control if not handled carefully.
Finally, legal enforceability is unsettled. A smart contract reliably executes its code, but whether that execution constitutes a legally binding contract, and how it interacts with consumer-protection, securities, and contract law, varies by jurisdiction and is still being worked out. Code can enforce an outcome; it cannot by itself guarantee that courts will recognise it. These limitations do not negate the technology's value, but they explain why audits, formal verification, insurance, and legal review have become standard practice around serious smart-contract deployments.
8. History and Evolution of Blockchain Technology
- 1982David ChaumSystems run by groups that do not trust each other
- 1991Haber and StornettaFirst cryptographically sealed chain of documents
- 1997HashcashAdam Back invents proof of work to fight spam
- 2008Bitcoin whitepaperSatoshi Nakamoto publishes 9 pages that change everything
- 2009Genesis blockThe first real blockchain is born
- 2015EthereumSmart contracts arrive on a public network
- 2016The DAOA hack ends in a hard fork: Ethereum Classic is born
- 2020DeFi SummerBillions flow into decentralised finance protocols
- 2022The MergeEthereum moves to Proof of Stake and cuts its energy use by 99.95%
- 2024-25ETFs, MiCA and stablecoinsUS spot Bitcoin ETFs, MiCA in force and stablecoins above $300B
From 1982 to 2025: the history of blockchain in 10 moments
8.1 The Pre-Bitcoin Foundations (1980s–2008)
Blockchain did not appear from nowhere; it assembled decades of cryptographic research. In 1982, cryptographer David Chaum's dissertation explored computer systems that could be established and maintained by mutually suspicious groups, an early articulation of the problem blockchains would later solve. Chaum went on to pioneer digital cash concepts that influenced the entire field.
In 1991, researchers Stuart Haber and W. Scott Stornetta published work on how to time-stamp digital documents so they could not be backdated or tampered with, chaining records together cryptographically, widely regarded as the first description of a cryptographically secured chain of blocks. In 1992, they incorporated Merkle trees into the design, allowing many documents to be collected into a single block efficiently, a direct ancestor of how modern blocks summarise transactions.
In 1997, Adam Back introduced Hashcash, a proof-of-work system originally designed to combat email spam by requiring a small computational cost per message. This proof-of-work concept would later become the engine of Bitcoin mining. In 2004, Hal Finney built Reusable Proof of Work (RPOW), a system that extended these ideas toward a usable token of value. By 2008, all the essential ingredients, cryptographic hashing, chained time-stamped records, Merkle trees, and proof of work, existed; what was missing was a design that combined them into a fully decentralised, double-spend-resistant system without any trusted party.
8.2 The Bitcoin Whitepaper and Blockchain's Birth (2008–2009)
In October 2008, a person or group using the pseudonym Satoshi Nakamoto published a nine-page whitepaper titled "Bitcoin: A Peer-to-Peer Electronic Cash System." It described how to combine proof of work, a distributed ledger, and economic incentives so that a network of untrusting participants could agree on a transaction history and prevent double-spending without any central authority. This was the moment the blockchain, as we understand it, was conceived.
In January 2009, Nakamoto mined the genesis block, Block 0, the first block of the Bitcoin blockchain and the first real blockchain in existence. Embedded in the genesis block was a line of text: "The Times 03/Jan/2009 Chancellor on brink of second bailout for banks," a reference to a newspaper headline of that day. The message served both as a timestamp proving the block was not created earlier and as a pointed comment on the fragility of the traditional banking system that Bitcoin was designed to offer an alternative to.
Days later, on 12 January 2009, the first Bitcoin transaction took place: Satoshi Nakamoto sent bitcoin to Hal Finney, the cryptographer who had built RPOW years earlier. A technology that had lived only in research papers and mailing lists was now running live, recording real transactions on a public, decentralised ledger.
8.3 Early Adoption and Altcoin Era (2010–2014)
For its first year, Bitcoin had no market price. That changed in 2010 with the first known real-world purchase: a programmer paid 10,000 BTC for two pizzas, an event now celebrated annually as Bitcoin Pizza Day and a vivid reminder of how early and uncertain the technology's value was. (Those values have, of course, fluctuated wildly since, and crypto-assets can lose value.)
In 2011, the first alternative cryptocurrencies, or altcoins, emerged, including Litecoin and Namecoin, as developers began experimenting with variations on Bitcoin's design and exploring uses for blockchain beyond simple payments. The idea that a blockchain could do more than move a single currency started to take hold.
In 2013, a young programmer named Vitalik Buterin published the Ethereum whitepaper, proposing a blockchain with a built-in programming language, a world computer on which anyone could deploy smart contracts and decentralised applications. This vision of a programmable blockchain would prove enormously influential. In 2014, the Ethereum project ran a crowdsale to fund development, and Ripple (XRP) gained attention for targeting cross-border interbank payments, signalling early institutional interest in the technology.
8.4 The Smart Contract Revolution and Enterprise Blockchain (2015–2018)
In July 2015, the Ethereum mainnet launched, and smart contracts moved from concept to reality. Developers could now deploy programmable logic to a public blockchain, laying the groundwork for DeFi, NFTs, tokenization, and much of what followed.
Also in 2015, the Linux Foundation launched the Hyperledger project, an umbrella for enterprise-grade, permissioned blockchain frameworks aimed at businesses that wanted distributed-ledger benefits without a public, permissionless network. Enterprise blockchain had arrived as a serious field.
In 2016, The DAO hack and the ensuing Ethereum hard fork, which split the network into Ethereum and Ethereum Classic, became a watershed governance moment, forcing the community to confront what immutability really meant and who ultimately controls a decentralised network. In 2017, the Initial Coin Offering (ICO) boom saw a wave of projects raise funds by issuing tokens, the CryptoKitties craze famously congested Ethereum by showing how a single popular application could strain the network, and Bitcoin's price surged toward roughly $20,000, drawing mainstream attention. By 2018, enterprise consortia such as R3 and the Enterprise Ethereum Alliance proliferated, and regulators worldwide intensified their scrutiny of the sector, setting the stage for the compliance-focused era to come.
8.5 Maturation, DeFi, NFTs, and Layer-2 (2019–Present)
From 2019 onward, blockchain matured from speculative frontier to institutional agenda. Central banks began serious experiments with central bank digital currencies (CBDCs), and Facebook announced its Libra project (later renamed Diem), which, though it never launched, galvanised policymakers worldwide to take digital money seriously.
In 2020, "DeFi Summer" saw billions of dollars locked into decentralised lending, trading, and yield protocols, demonstrating that smart-contract-based finance could operate at scale, while Ethereum launched its Beacon Chain, the proof-of-stake layer that would later merge with the main network. In 2021, the NFT market exploded into public consciousness (a Beeple digital artwork sold for around $69 million), El Salvador became the first country to adopt Bitcoin as legal tender, and Layer-2 rollups gained real traction as a scaling solution.
A defining technical milestone came next. The Merge, Ethereum's transition from Proof of Work to Proof of Stake on 15 September 2022, cut the network's energy use by about 99.95%. Then the institutional door opened wider: on 10 January 2024, the US SEC approved applications for 11 Bitcoin spot exchange-traded funds (ETFs). Notably, the regulator was careful to frame the move narrowly: as Gensler emphasized, "while we approved the listing and trading of certain spot bitcoin ETP shares today, we did not approve or endorse bitcoin." That decade-plus arc, from a nine-page whitepaper to regulated investment products on major exchanges, captures how far the technology has travelled, even as questions of regulation, scalability, and governance remain very much open. In Europe, the Markets in Crypto-Assets Regulation (MiCA) has applied since December 2024, giving the region one of the world's most comprehensive frameworks for crypto-assets, which is a central reason institutions across Europe and Latin America are now moving from experiments to production.
The largest conference on crypto and digital assets
Banks, fintechs and the crypto ecosystem at the same table. Two editions in 2027:
9. Benefits of Blockchain Technology
Stepping back from the mechanics, it is worth stating plainly why organisations invest in blockchain at all. The benefits cluster around a few durable themes.
Trust without intermediaries. The core value proposition is enabling parties who do not trust each other to transact reliably without a central middleman, which can reduce cost, counterparty risk, and settlement delays.
Transparency and auditability. On the right architecture, every transaction is recorded on a shared, tamper-evident ledger, giving auditors, regulators, and counterparties a single source of truth and dramatically simplifying reconciliation.
Security and integrity. Cryptographic linking and distributed replication make records extremely resistant to tampering and eliminate the single point of failure inherent in a centralised database.
Efficiency and speed in the right contexts. By automating processes with smart contracts and removing layers of intermediation, blockchain can compress settlement that traditionally takes days into minutes, particularly in cross-border payments and securities settlement.
Programmability. Smart contracts turn static records into automated workflows, enabling entirely new products such as programmable money, tokenized assets, and self-executing agreements.
These benefits are real but context-dependent. A blockchain is not automatically better than a well-run centralised database; it earns its keep specifically when multiple parties who do not fully trust each other need a shared, tamper-evident record. Where a single trusted operator suffices, a traditional database is usually simpler and faster.
10. Blockchain Use Cases Beyond Cryptocurrency
While cryptocurrency was the first application, the technology now underpins a broad range of use cases.
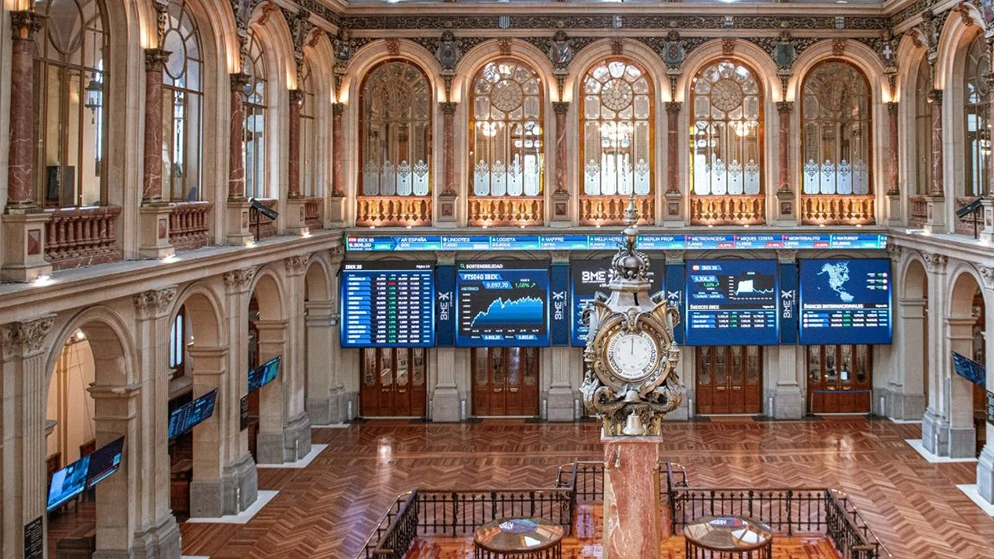
The Madrid Stock Exchange, home of the MERGE Madrid 2026 Institutional Summit, where banks, regulators and infrastructure providers discuss how to take blockchain into production
Payments and remittances. Stablecoins and blockchain rails can move value across borders quickly and at lower cost than correspondent banking, which is why banks are actively exploring and, in some cases, issuing their own stablecoins.
Tokenization of real-world assets. Bonds, funds, real estate, and other assets can be represented as tokens, enabling fractional ownership, faster settlement, and new forms of liquidity. This is one of the most closely watched institutional applications in regulated markets.
Supply chain and provenance. Blockchain can track goods from origin to shelf, giving consumers and regulators verifiable provenance and helping combat counterfeiting and fraud.
Identity and credentials. Self-sovereign identity and verifiable credentials let individuals prove facts about themselves (age, qualifications, licences) without exposing unnecessary personal data.
Healthcare, energy, and public records. Consortium and permissioned chains are being used for shared medical records, energy trading, land registries, and other domains where multiple parties need a common trusted ledger.
DeFi and financial infrastructure. Lending, trading, derivatives, and asset management can run as open protocols, and traditional institutions are increasingly experimenting with permissioned versions of these primitives.
The common thread is that blockchain adds value wherever multiple parties need to share and trust a common record without ceding control to a single operator, which is exactly the convergence of traditional finance and the digital economy that institutions across Europe and Latin America are now navigating.
11. Notable Blockchain Platforms, and Blockchain vs. Bitcoin
A frequent point of confusion deserves direct treatment: blockchain is the underlying technology, while Bitcoin is one specific application of it. Bitcoin is a cryptocurrency that runs on a blockchain, but blockchain also powers Ethereum's smart contracts, enterprise supply-chain systems, and much more. All bitcoin involves blockchain, but not all blockchain involves bitcoin. Saying "blockchain" when you mean "Bitcoin" is like saying "the internet" when you mean "email."
The major platforms each occupy a distinct niche. Bitcoin is the original and most secure Proof-of-Work blockchain, optimised as a decentralised store of value and settlement network. Ethereum is the leading smart-contract platform, now secured by Proof of Stake, and the foundation of most DeFi, NFTs, and tokenization. Solana prioritises high throughput and low fees using its Proof-of-History innovation alongside Proof of Stake. Other notable public networks include Cardano, Avalanche, Polkadot, and Polygon (a widely used Ethereum scaling ecosystem). On the enterprise and consortium side, Hyperledger Besu, which is Ethereum-compatible, has become the most common choice, ahead of classic permissioned frameworks such as Hyperledger Fabric, R3 Corda and Quorum used in finance and supply chains.
Each platform embodies different choices along the trade-offs described throughout this guide: decentralisation versus speed, openness versus control, security versus cost. There is no universal winner; the right platform depends entirely on the use case, the regulatory context, and the parties involved. Importantly, none of this is a recommendation to buy or hold any particular asset; crypto-asset values fluctuate and can lose value, and anyone evaluating investment exposure should consult the relevant risk information at mmerge.io/riesgos.
12. Challenges and Limitations of Blockchain
For all its promise, blockchain faces genuine, unresolved challenges that institutions weigh carefully.
Scalability. Base-layer public blockchains process far fewer transactions per second than centralised payment networks, which is why Layer-2 rollups, sidechains, and alternative consensus designs exist. The "blockchain trilemma," the difficulty of achieving decentralisation, security, and scalability simultaneously, remains the field's central engineering tension.
It is hard to maximise all three at once. Bitcoin and Ethereum prioritise security and decentralisation; Solana and private networks give up some decentralisation (fewer nodes, or more demanding ones) to gain speed.
That is why Bitcoin and Ethereum look for scalability off the main chain, in Layer-2s and rollups, without giving up the security of the base layer.
The blockchain trilemma
Energy use. Proof-of-Work chains consume substantial energy, though the shift of major networks like Ethereum to Proof of Stake has shown that this is a design choice, not an inherent property of all blockchains.
Regulatory uncertainty. Rules vary sharply across jurisdictions and continue to evolve. Frameworks like the EU's MiCA bring welcome clarity in Europe, but global fragmentation and the unsettled legal status of smart contracts and tokens create compliance complexity.
User experience and key management. Self-custody places the full burden of security on the user; a lost private key means permanently lost funds, and the overall experience remains daunting for non-specialists.
Interoperability. With many chains operating in parallel, moving assets and data securely between them is hard, and cross-chain bridges have been a recurring target for major exploits.
Smart-contract and systemic risk. As the DAO and numerous later incidents show, code vulnerabilities, oracle manipulation, and concentrated infrastructure can cause large losses. Security incidents should be reported factually and understood as reminders that the technology is still maturing.
None of these challenges is necessarily fatal, and each is the subject of intense research and investment. But an honest assessment of blockchain requires holding its real benefits and its real limitations in view at the same time, which is precisely the balanced, evidence-led perspective institutions bring to the table.
MERGE Institute
Learn crypto and digital assets from the leaders of the ecosystem
A 12-week programme, taught in Spanish by working professionals. Blockchain architecture, consensus and scalability are covered in Module 6.
Try a free class →Key Takeaways
- A blockchain is a distributed, cryptographically linked, append-only ledger maintained across many independent nodes, making it the most prominent form of distributed ledger technology; all blockchains are DLTs, but not all DLTs are blockchains.
- Its core properties, decentralisation, transparency, immutability, and security, come from the interaction of cryptographic hashing, public-key signatures, and consensus mechanisms such as Proof of Work and Proof of Stake, each with distinct trade-offs between energy use, speed, and decentralisation.
- Networks range from fully public and permissionless (Bitcoin, Ethereum) to private and consortium chains used by enterprises and banks; the right choice depends entirely on the use case and regulatory context.
- Smart contracts add a programmable layer that powers DeFi, NFTs, tokenization, and automated agreements, but they carry real risks, including code vulnerabilities, the oracle problem, and unsettled legal enforceability.
- "Immutable" is better understood as tamper-evident and tamper-resistant: as the 2016 DAO hard fork showed, a determined community can override even the ledger itself, so governance matters as much as cryptography.
If you want to go deeper into how banks, regulators, and infrastructure teams are putting this into practice, MERGE Institute offers a non-university executive certificate program built with practitioners, and you can explore its structure and start with a free class at mmerge.io/merge-institute.
Frequently Asked Questions
What is the difference between blockchain and Bitcoin?
Blockchain is the underlying technology, a distributed, cryptographically secured ledger, while Bitcoin is one specific cryptocurrency that runs on a blockchain. Bitcoin was the first real-world use of blockchain, launched with the genesis block in January 2009, but the same technology now powers Ethereum's smart contracts, enterprise supply-chain systems, tokenized securities, and much more. In short, Bitcoin is an application of blockchain, not a synonym for it.
Is blockchain the same as distributed ledger technology (DLT)?
Not exactly. Distributed ledger technology is the broad category of any system that records data across multiple locations simultaneously without a central authority. Blockchain is one type of DLT, the one that organises data into cryptographically linked blocks. Other forms of DLT, such as Directed Acyclic Graphs (used by IOTA and Hedera) and Hashgraph, distribute records differently. So every blockchain is a DLT, but not every DLT is a blockchain.
How does a blockchain stay secure?
Security comes from several layers working together: public-key cryptography and digital signatures prove who authorised each transaction, cryptographic hashing links blocks so that altering one visibly breaks the chain, and consensus mechanisms make dishonest participation economically prohibitive by requiring attackers to control a majority of hash power or staked value. The main threat is a 51% attack, which is practically infeasible on large networks like Bitcoin but has succeeded against smaller chains, for example Ethereum Classic in 2020.
What is the difference between a public and a private blockchain?
A public blockchain (such as Bitcoin or Ethereum) is open and permissionless: anyone can join, read the ledger, transact, and participate in consensus, with full decentralisation but slower speeds and less privacy. A private blockchain is controlled by a single organisation and is permissioned: participants are vetted and access is gated, trading decentralisation for speed, privacy, and control. A consortium blockchain sits in between, governed jointly by a defined group of organisations, which is a common model in regulated finance.
Did Ethereum's switch to Proof of Stake really cut its energy use?
Yes. The Merge completed Ethereum's transition to proof-of-stake consensus in September 2022, officially deprecating proof-of-work and reducing its energy consumption by about 99.95%. The change replaced energy-intensive mining with a system where validators stake capital as collateral, demonstrating that high energy use is a design choice specific to Proof-of-Work chains rather than an inherent property of all blockchains.
Are smart contracts legally binding?
It depends on the jurisdiction, and the law is still developing. A smart contract reliably executes its code, but whether that execution amounts to a legally enforceable contract, and how it interacts with securities, consumer-protection, and contract law, varies widely around the world. Many serious deployments therefore pair smart contracts with traditional legal documentation and review. For anything involving regulatory or legal questions, you should consult a qualified professional, as this article is educational and not legal or investment advice.